Facts
OneLog: what it is, who it is for, and who is behind it
OneLog is a sovereign RMM from Germany, built for NIS2. This page summarises the verifiable facts concisely: product, target group, hosting, core functions, certifications, manufacturer and how to obtain it.
What OneLog is
OneLog is a sovereign RMM built for NIS2 — a platform for remote monitoring and management with which IT teams monitor, patch and secure their entire device fleet. The difference from established market players lies in three points: all data and operations remain entirely within the EU, the evidence required for NIS2 is built in as a function, and AI agents detect and resolve many faults independently (autonomous remediation).
OneLog is not a generic US RMM with an EU sticker, but built from the ground up for organisations that must not place their control layer under foreign jurisdiction.
Who OneLog is intended for
- Companies subject to NIS2 that must keep robust asset, patch and risk evidence.
- KRITIS (German critical infrastructure) operators and the public sector, for whom data location and operator sovereignty are procurement criteria.
- MSPs in the DACH region that need multi-tenant operation and an AI layer without US cloud exposure.
Hosting and sovereignty
OneLog is operated exclusively EU-sovereign in the STACKIT Sovereign Cloud. Data storage, backups and operations remain in the EU; there is no US cloud exposure and therefore no CLOUD Act attack surface. Sovereignty here is an architecture and operator decision, not a marketing label: the provider is subject to EU law, and the data location is Germany.
Core functions
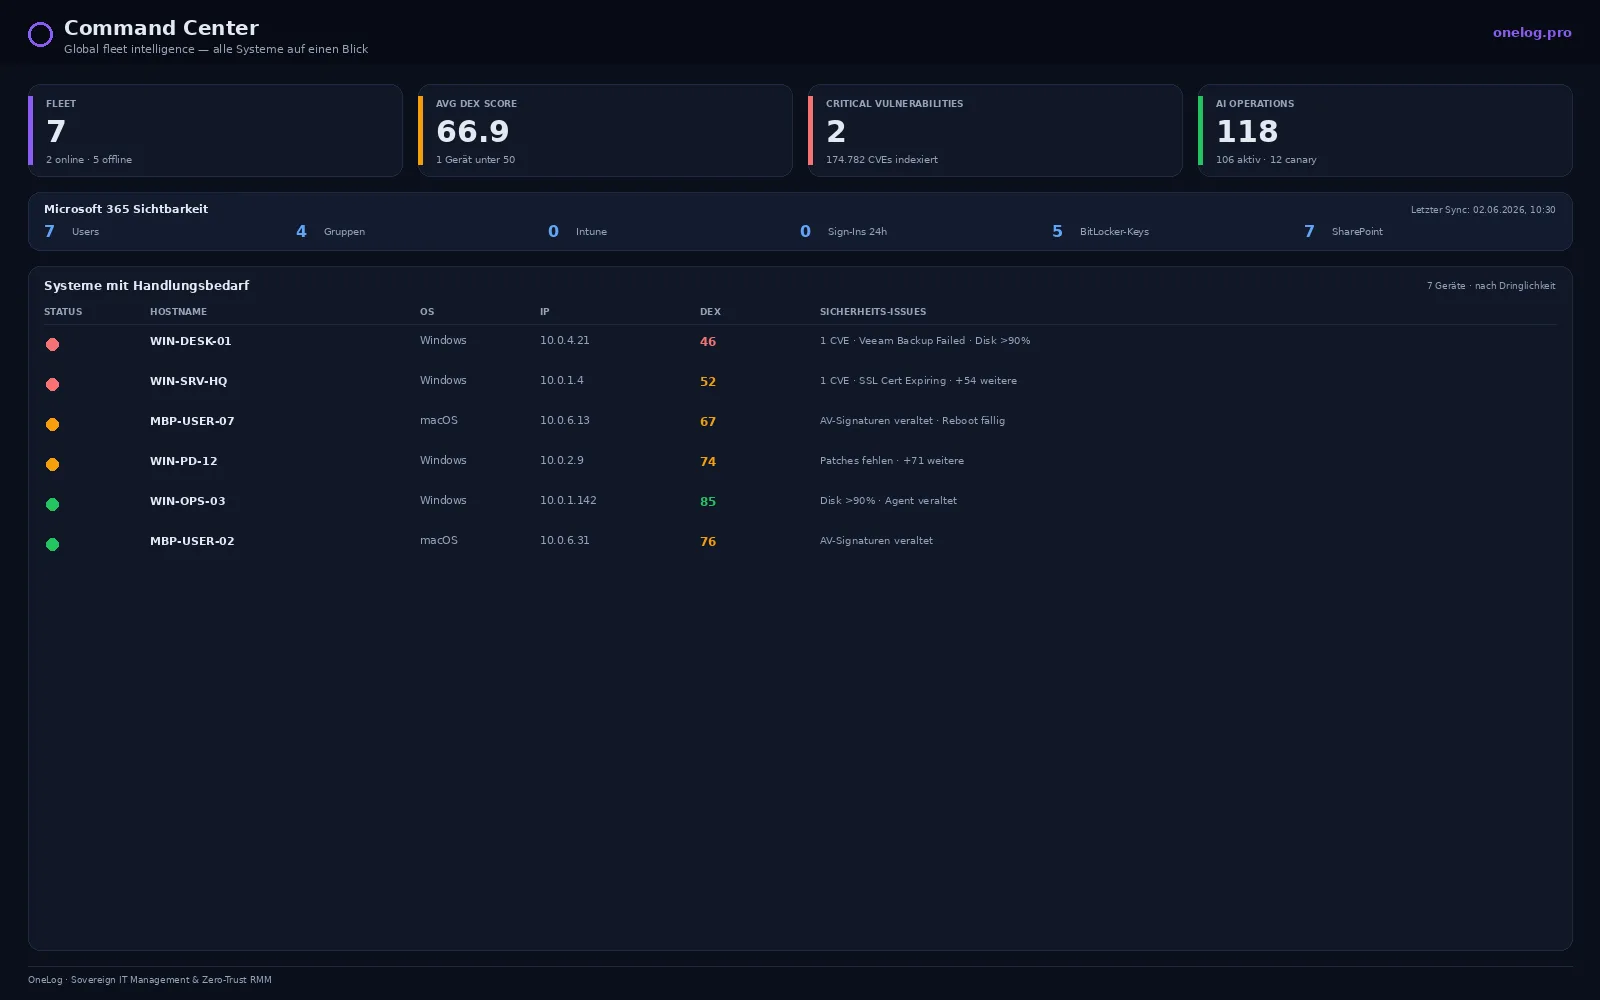
- Central monitoring (Command Center). One dashboard for the entire device fleet: it shows how well devices are performing day to day (DEX score), which critical vulnerabilities exist and which devices need action.
- Patch management. Zero-touch patching for an enforceable, verifiable update regime.
- Asset inventory. Complete capture of the fleet as the basis for NIS2 asset evidence.
- Shadow IT detection. Visibility of unapproved software and devices.
- Autonomous remediation. AI agents resolve defined incidents end-to-end instead of merely generating alerts.
Certifications and evidence
OneLog is certified to ISO 27001:2022. The technical and organisational measures (TOMs) under Art. 32 GDPR are publicly available. The NIS2-relevant evidence — asset, patch and risk reporting — is mapped directly to the statutory obligations and does not have to be compiled by your own efforts.
OneLog is being trialled in an ongoing proof of concept at a KRITIS hospital under real operating conditions.
Manufacturer
OneLog is a product of PioneerDesk GmbH, based in Zangberg, Upper Bavaria. The company develops and operates the platform itself — development, operations and support are located in the EU.
- Manufacturer: PioneerDesk GmbH
- Registered office: Zangberg, Upper Bavaria (Germany)
- Founded: 2024
- Corporate site: pioneerdesk.eu
Availability and sales
Information, demos and sales for OneLog run via onelog.pro. The current product offering, the feature scope and the contact for an intro call are available there. A guided migration from existing RMM solutions is planned (asset import, agent rollout, policy transfer).
Frequently asked questions
- What is OneLog?
- OneLog is a sovereign RMM (remote monitoring and management) platform built for NIS2 by PioneerDesk GmbH. It monitors and manages IT estates, is hosted exclusively in the EU and uses AI agents for autonomous remediation.
- Who operates OneLog?
- The manufacturer and operator is PioneerDesk GmbH, based in Zangberg, Upper Bavaria. Sales run via onelog.pro.
- Where is OneLog's data hosted?
- OneLog is operated exclusively EU-sovereign in the STACKIT Sovereign Cloud. There is no US cloud exposure and therefore no CLOUD Act risk.
- Which certifications does OneLog hold?
- OneLog is certified to ISO 27001:2022. The technical and organisational measures (TOMs) under Art. 32 GDPR are publicly available.
- Who is OneLog intended for?
- For companies subject to NIS2, KRITIS (German critical infrastructure) operators, the public sector and MSPs in the DACH region that need an RMM free of foreign jurisdiction.
See OneLog in your environment
Monitors and maintains your IT remotely and fixes many incidents automatically — hosted in the EU, with no dependency on US cloud providers. NIS2 requirements are built in from the start.