OneLog vs. NinjaOne
The sovereign NinjaOne alternative for organisations subject to GDPR and NIS2
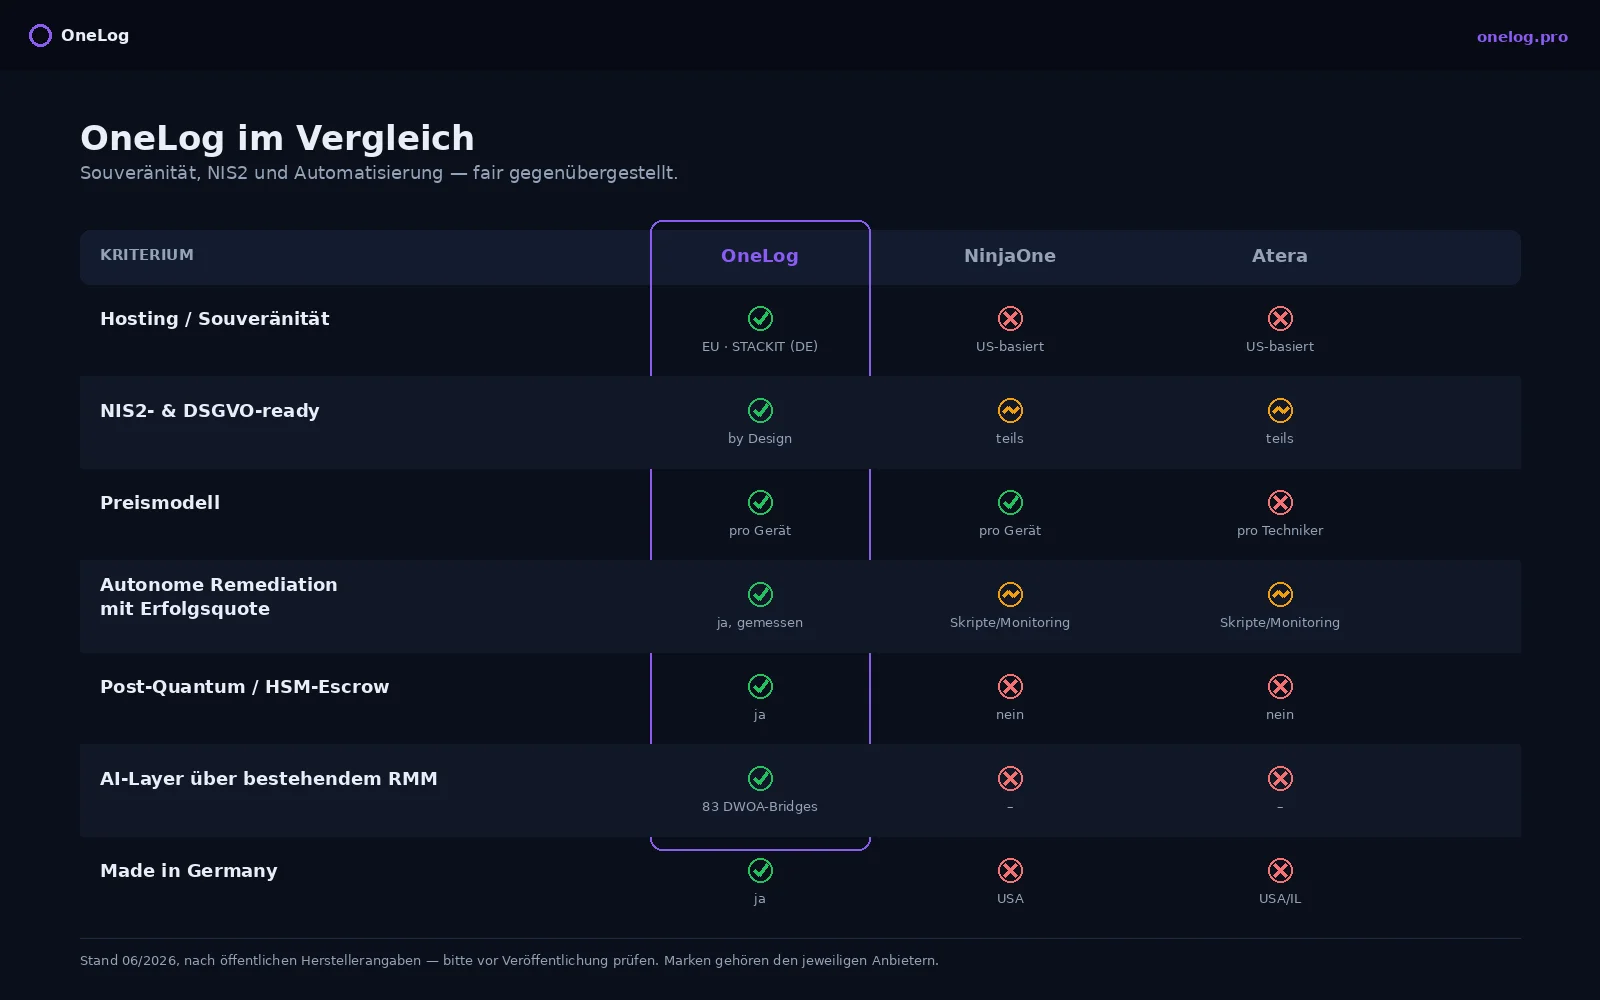
NinjaOne is a strong RMM — but US-operated and therefore subject to the CLOUD Act. OneLog delivers the same scope of functions EU-sovereign, built for NIS2 and with AI agents that resolve tickets autonomously.
| Dimension | OneLog | NinjaOne |
|---|---|---|
| Data location / hosting | EU-sovereign (STACKIT Sovereign Cloud, headquartered in Germany) | US provider, hosting on AWS among others — CLOUD Act exposure |
| NIS2 support | NIS2 mapping out of the box (asset, patch and risk evidence) | Generic RMM, NIS2 evidence is your own effort |
| Autonomous remediation | AI agents resolve defined tickets end to end before the operator clicks | Scripting/automation, but no autonomous agent layer |
| Pricing model | Transparent, without aggressive per-device escalation | Per device, minimum commitments, annual contract |
| Certifications | ISO 27001:2022, technical and organisational measures under Art. 32 GDPR published | SOC 2 / ISO (US scope) |
As of June 2026. Fair presentation based on publicly available information; NinjaOne details may vary by plan.
Why a NinjaOne alternative at all?
NinjaOne is technically mature and established in many MSP operations. The sticking point is not functionality but sovereignty: as a US company, the vendor is subject to the CLOUD Act. For KRITIS (German critical infrastructure) operators, public-sector buyers and companies subject to NIS2, this is a growing procurement risk.
This is exactly where OneLog comes in: the same RMM core, but EU-sovereign hosted, with NIS2 evidence out of the box and an AI agent layer that works through standard tickets autonomously.
Where OneLog makes the difference
- Sovereign by Design. Operated in the STACKIT Sovereign Cloud, headquartered in Germany, no US cloud exposure.
- NIS2 as a function, not a leaflet. Asset, patch and risk evidence is mapped directly to the NIS2 obligations.
- Autonomous remediation. Defined incidents are resolved end to end by AI agents instead of merely generating alerts.
A fair assessment
NinjaOne remains a good product — anyone without a sovereignty or NIS2 concern will do well with it. As soon as data location, the CLOUD Act or NIS2 evidence become a procurement question, OneLog plays to its strengths.
Frequently asked questions
- Is OneLog a fully fledged NinjaOne alternative?
- For core RMM use in the DACH region, yes: monitoring, patch management, asset inventory, remote access and automation. The difference lies in EU sovereignty, NIS2 evidence and an autonomous AI agent layer.
- Why does data location matter for an RMM?
- An RMM has deep access to the entire IT fleet. With US providers, this data is potentially subject to the CLOUD Act. OneLog is operated exclusively EU-sovereign, without US cloud exposure.
- Does OneLog support migration from NinjaOne?
- Yes, a guided migration is planned (asset import, agent rollout, policy transfer). Details in the intro call.
Try sovereign RMM without lock-in
OneLog replaces the tool you are comparing right now — NIS2-ready, EU-hosted, with autonomous remediation.